
President Donald Trump’s AI task force says it will ensure that the government is protecting Americans from the powerful technology’s cybersecurity risks. The only problem: It’s made no mention of the federal agency in charge of handling those risks.
The senior government officials leading Trump’s newest AI initiative — who regularly promote AI’s benefits and say comparatively little about its harms — have essentially ignored the Department of Homeland Security’s Cybersecurity and Infrastructure Security Agency in their public remarks about the task force. The group has teams focused on critical infrastructure security and incident reporting, areas in which CISA has more expertise than any other agency, but CISA is not leading those teams and might not even be participating in them.
CISA’s conspicuous absence from the task force’s work could presage serious problems. Without CISA’s deep involvement, experts told Cybersecurity Dive, the task force risks producing half-baked or redundant AI security guidance and requirements that confuse or overburden businesses embracing the technology.
Such outcomes could end up undermining, rather than strengthening, the business community’s focus on AI security challenges at a time when the fast-moving technology is increasingly magnifying digital threats.
The task force sidelining CISA “would be like a football team leaving its defense at home for the big game,” said Jeff Greene, a former top official at CISA and the National Security Council.
Forum for urgent action
The U.S. government’s approach to AI has evolved dramatically along with the changing threat landscape. In early October, Trump created a task force to promote AI while limiting its harms, arguing that the technology could be “bigger than the Industrial Revolution.” Trump’s move came after a monthslong period during which virtually every frontier AI lab announced that their leading models had escaped their safeguards and, in some cases, hacked into other companies.
Cybersecurity experts, many of whom had warned for years that AI would empower hackers to conduct attacks with unprecedented ease and sophistication, said the loss-of-control incidents highlighted gaps in the oversight mechanisms designed to protect Americans from dangerous technology.
The task force, led by Director of National Intelligence Jay Clayton, is designed in part to address those gaps. The group has three main workstreams: Emil Michael, the Pentagon’s top research official, is supervising the creation of early-warning protocols for security incidents; Federal Trade Commission Chair Andrew Ferguson is handling consumer protection and law enforcement; and Office of Personnel Management (OPM) Director Scott Kupor is handling critical infrastructure security and workforce impacts.
The Trump administration generally has rejected technology regulation, but in mid-October, the White House began telling news outlets that it now expected AI labs to report loss-of-control incidents and other examples of unsafe behavior. “[AI] companies must immediately disclose incidents involving their models and follow with swift, decisive action to remedy any and all harm,” Clayton, Ferguson, Kupor and Michael said in a statement to Cybersecurity Dive.
At the same time, Trump’s financial interests in the AI industry and his administration’s focus on beating China in the AI race have created incentives for him to minimize the technology’s security risks.
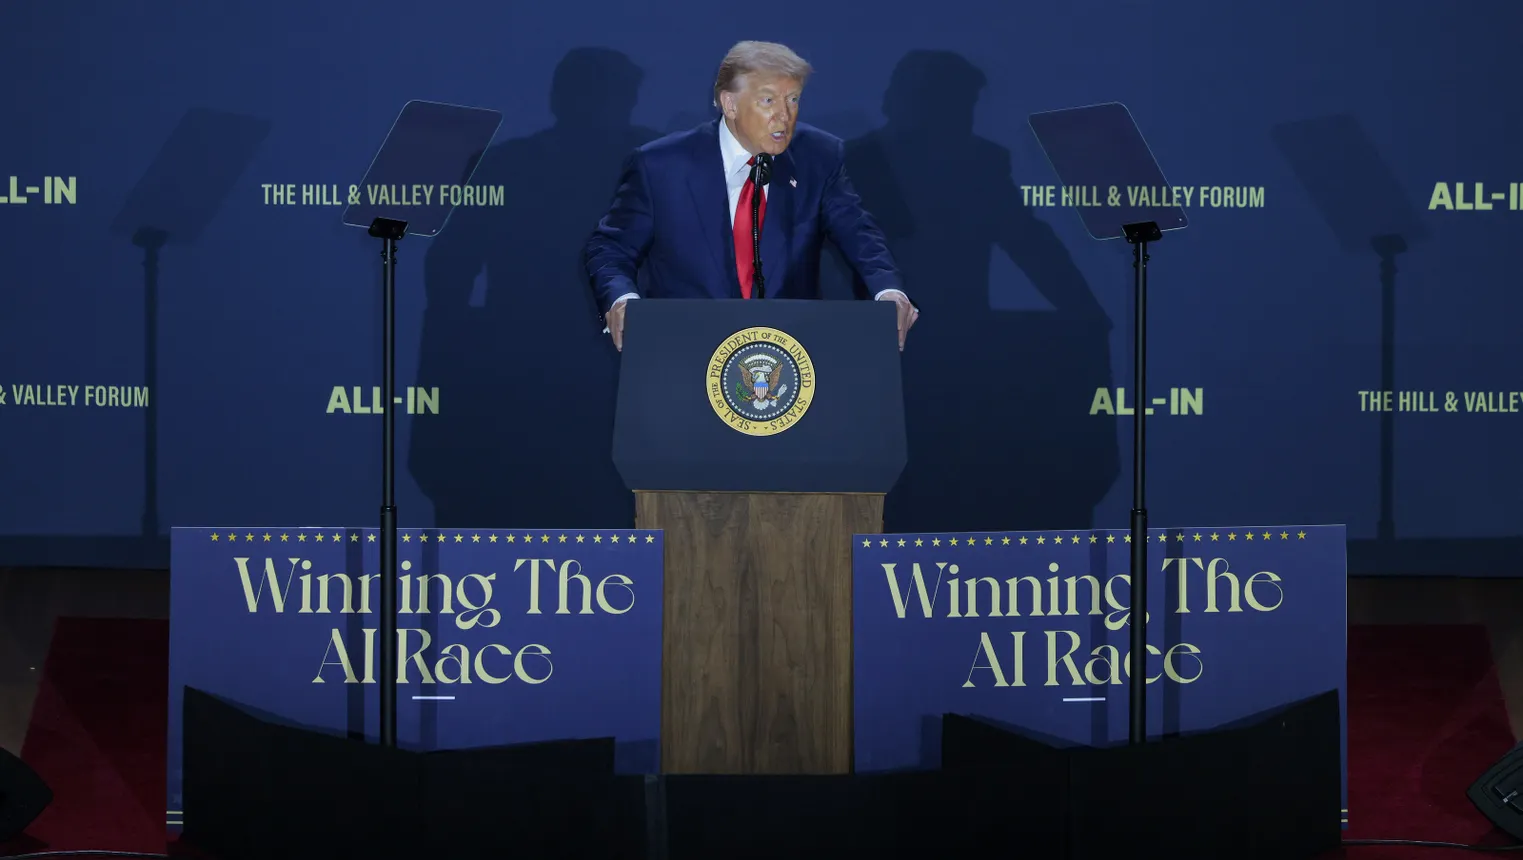
President Donald Trump speaks during the “Winning the AI Race” summit hosted by the All‑In Podcast and the Hill and Valley Forum in Washington, D.C., on July 23, 2025.
Chip Somodevilla via Getty Images
Question mark on CISA’s role
With an ambitious agenda, the task force will only be as successful as the experts it consults. But while cybersecurity is a major focus of the task force — it was one of the three topics the task force recently asked the President’s Council of Advisers on Science and Technology to study — no one associated with the group has suggested that it is consulting with CISA or even acknowledged the agency’s lead role on cybersecurity.
The omission is notable because the Trump administration claims it is rebuilding CISA after decimating the agency’s workforce and curtailing its activities, changes that alarmed CISA’s partners in the critical infrastructure community.
The White House declined to comment on CISA’s role in the AI task force. It referred Cybersecurity Dive’s inquiry to OPM, which provided a statement from Kupor that did not mention CISA: “The [AI] Force will be partnering closely with all of our colleagues across government to ensure the best outcomes for the American people.” CISA did not respond to several requests for comment about its role in the task force.
It is essential for CISA to be heavily involved in the task force’s AI security work, according to cybersecurity experts and former agency employees.
“CISA has spent the last several years investing in their AI expertise and capabilities, specifically on the intersection of AI and cybersecurity — how to secure AI systems, and how to use AI for cybersecurity operations,” said Daniel Bardenstein, a former senior technology strategy adviser at CISA. “Not only can they offer technical expertise, but they bring a deep set of relationships to critical infrastructure and private-sector security operators who can share their experience and concerns with AI security as well.”
The task force should tap CISA to “help lead and enable” its work on incident reporting and critical infrastructure protection, said Matt Altomare, a former top threat-hunting official at CISA. Altomare, now the senior director of cybersecurity programs at the Aspen Institute, noted that Congress designated CISA as the federal government’s national coordinator for critical infrastructure security and resilience.
A CISA employee, who requested anonymity to speak freely, also argued that the agency should have a role in the task force that suited its statutory mission.
“CISA was created to be the organization to help manage the risk and defend the nation’s critical infrastructure,” the employee said. “The position CISA [holds] should be congruent with those ideals.”
“[CISA brings] a deep set of relationships to critical infrastructure and private-sector security operators who can share their experience and concerns with AI security as well.”

Daniel Bardenstein
CEO, Manifest; Former Chief of Tech Strategy, CISA
A natural fit for CISA’s mission
The task force should lean heavily on CISA for the cybersecurity activities it performs, experts said.
The agency can be most useful in sharing guidance with the critical infrastructure community and liaising between infrastructure operators and other federal agencies. “CISA is the agency best positioned to understand both the risks AI poses to critical infrastructure and the ways it can make that infrastructure safer,” said Lauren Zabierek, a former senior policy adviser at CISA.
Because it is impossible to block every AI-powered attack, Greene said, the task force’s focus should be on encouraging infrastructure operators to be resilient to those attacks, something that CISA is already doing with its CI Fortify initiative.
In addition, CISA has spent years analyzing software security and fostering greater awareness of those issues among infrastructure operators. AI is just another form of software that creates risks (such as going rogue or accelerating hackers’ attacks) and opportunities (such as speeding up the creation of memory-safe code).
CISA “has long been at the forefront of engaging with critical infrastructure operators around cybersecurity,” Bardenstein said. “Adding AI-related security issues to that scope is a wise and effective decision.”
The alternative, he added, “would be having a different government agency handle that, which would only make things harder on [infrastructure] operators.”
As the task force considers new standards for how frontier labs should report incidents to the government, CISA’s expertise with incident response — and with developing guidelines for it — could be invaluable. “There’s little reason to ignore this existing strength and past performance,” Bardenstein said.
CISA is developing broader incident-reporting rules for the critical infrastructure community pursuant to the 2022 Cyber Incident Reporting for Critical Infrastructure Act (CIRCIA). And in mid-October, CISA and NIST published guidance for how AI labs should protect against loss-of-control incidents.
“CISA is the agency best positioned to understand both the risks AI poses to critical infrastructure and the ways it can make that infrastructure safer.”
Lauren Zabierek
Cofounder, Foundation Layer Institute; Former Senior Adviser, CISA
Risking “minimal lasting impact”
There are early indications that the task force does not intend to rely much on CISA.
Despite CISA’s deep experience with critical infrastructure security, the White House placed OPM’s Kupor in charge of liaising with infrastructure operators. That decision puzzled some experts, who said it ignored established systems. Others said there might be a rationale for Kupor’s prominent role, such as his background in venture capital. He was the first person hired at the VC firm Andreessen Horowitz, which has invested heavily in AI.
“The administration may be hoping that he provides a strong connection to AI expertise in the private sector,” Bardenstein said. “On the other hand, Silicon Valley VCs aren’t known to have a particularly strong relationship with critical infrastructure operators.”
Regardless, sidelining CISA could cause serious problems for the task force’s work.
Without CISA’s extensive industry partnerships, Zabierek said, the task force is likely to overlook “the [infrastructure] operators with the fewest resources, such as small utilities and rural hospitals,” leaving them out of a conversation that disproportionately affects them.
The Trump administration’s workforce downsizing has placed a strain on many of CISA’s relationships, but it still has stronger ties to a wider range of industry organizations than any other agency.
“Without trust and strong relationships, even the best-intentioned efforts by the government to collaborate with industry on cybersecurity will have minimal lasting impact,” said Bardenstein, who helped manage industry partnerships in the Hack the Pentagon bug-bounty program.
In addition, CISA’s other activities could suffer if it is not sufficiently tied into the task force. The group could end up recommending incident-reporting rules for AI systems that duplicate what CISA is doing with CIRCIA.
A second CISA employee, who also requested anonymity to speak freely, said that could force infrastructure operators to follow “different guidance or processes simply because something is ‘AI-related’ versus ‘cybersecurity-related,’ and those two issues are simply too interlinked to separate that way.”
At a higher level, sidelining CISA risks further demoralizing a workforce that has already endured two years of layoffs, program reductions and leadership turmoil.
“Even though CISA is actually still operating well, the headlines from the past few years have reduced the private sector’s confidence in their ability to achieve their mission,” Bardenstein said. “Omitting CISA from the task force will only further reduce that confidence and trust.”





